
Updated on November 11, 2026
Containers gained popularity in the 2010s because they allowed developers to run programs across environments, but deploying thousands of them could be chaotic. Enter Kubernetes, an orchestration platform that emerged to manage containers at scale. But Kubernetes itself, not just its containers, needs vulnerability scanning. How? What should that look like? From merging tools to spanning the development lifecycle as well as the Kubernetes environment and the containers it contains, we’re breaking it down.
What is Kubernetes Vulnerability Scanning?
Kubernetes vulnerability scanning is a security tactic that scrutinizes the Kubernetes environment, including:
- Cluster configuration: Checking for Kubernetes settings, permissions, and exposed services
- Kubernetes components: Scanning critical Kubernetes components like the control plane, API server, and
etcddatabase - Container images: Inspecting container images stored in registries or running in the cluster for outdated dependencies, vulnerabilities, and insecure libraries.
Kubernetes automated container scaling, deployment, and recovery — everything from updates to ensuring containers can always communicate with each other and users can always connect to a working container — so today, companies build and run apps faster and easier.
But the managerial powers of Kubernetes that give it control over how containers are deployed also present a new attack surface. And if attackers compromise Kubernetes itself, they can control the entire container environment.
While Kubernetes vulnerability scanning might suggest scanning at the level of orchestration for setup problems only, scanning containers themselves can be part of the discussion on Kubernetes vulnerability scanning. On the other hand, Kubernetes runtime security focuses on watching for live threats, whereas the broader Kubernetes security includes the tactics and strategies used to secure everything from the setup to live threat defense.
What Is a Kubernetes Scanner?
A Kubernetes scanner is a category of security tool that checks the Kubernetes environment for weaknesses attackers could exploit. Depending on the tool, that includes cluster configuration, control plane exposure, nodes, manifests, registries, and running workloads.
Scanners generally fall into a few types:
- Image scanners: Inspect container images in registries or the cluster for outdated dependencies, insecure libraries, and known CVEs
- Manifest and IaC misconfiguration scanners: Check Kubernetes files for risky settings before anything is deployed
- Cluster posture scanners: Review settings, permissions, exposed services, and components like the API server and
etcd - Node scanners: Assess the underlying servers for issues like missing patches or default credentials
- Runtime scanners: Watch live workloads for issues that only appear during execution, like container escapes or lateral movement
Results typically include CVEs, misconfigurations, policy violations, and exposed services, each with a severity rating and remediation guidance.
That scope separates a Kubernetes scanner from a container-only scanner, which looks at images but not at the cluster that orchestrates them.
Runtime and Kubernetes Vulnerability Scanning with Upwind
Upwind offers runtime-powered container scanning features so you get real-time threat detection, contextualized analysis, remediation, and root cause analysis that’s 10X faster than traditional methods.
Get a DemoThe Full Scope of K8s Vulnerabilities
A vulnerability is a weakness or flaw in a system that attackers can exploit. In the context of Kubernetes, vulnerabilities can occur at various levels — from container images to Kubernetes’ core components like its control plane, nodes, networking services, authorization checks, and admin tooling. Kubernetes CVEs disclosed since mid-2025 show that range. They include nodes able to delete themselves by adding an OwnerReference, nodes bypassing dynamic resource allocation authorization checks, cross-namespace pod creation via StatefulSet and ControllerRevision write permissions, and Windows-specific issues in subpath handling and kubectl cp. Publicly disclosed vulnerabilities are numbered and cataloged as CVEs (common vulnerabilities and exposures).
More of these flaws are identified and exploited all the time. That means organizations and vendors aren’t even currently aware of all the flaws in their systems. Vulnerabilities often come to light after a security incident, so identifying and re-engineering thousands of containers to accommodate new patches for new vulnerabilities, across thousands of instances, continually, is no simple task.
To secure Kubernetes effectively, it helps to understand its most common vulnerability categories, including:
Container Image Risks
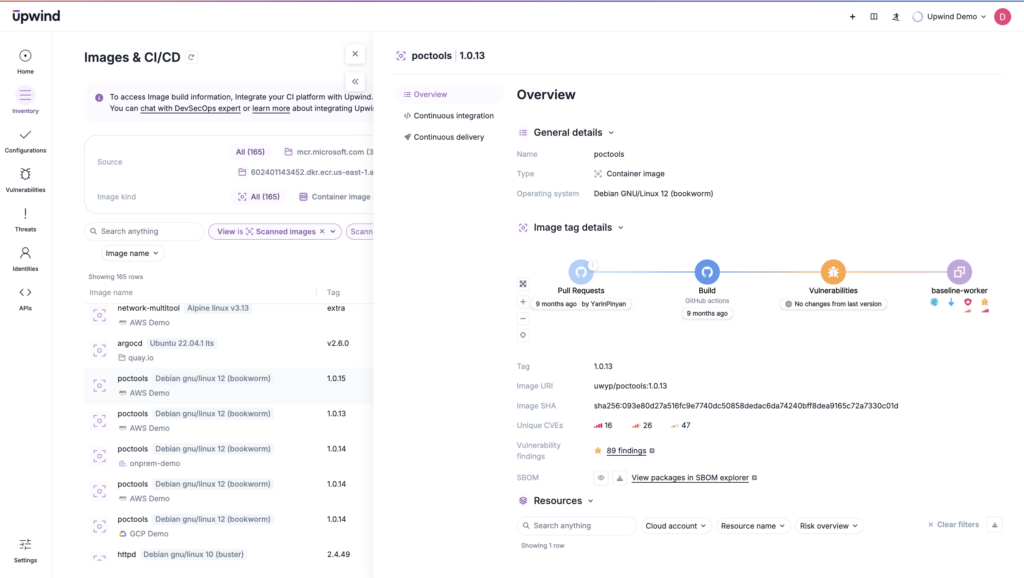
Container images vulnerabilities are an outsized category of flaws impacting Kubernetes. DevOps teams often use open-source components to build their container images, which is an inherently risky process because these images don’t necessarily follow best practices, so it’s easy for vulnerabilities to proliferate.
Configuration Weaknesses
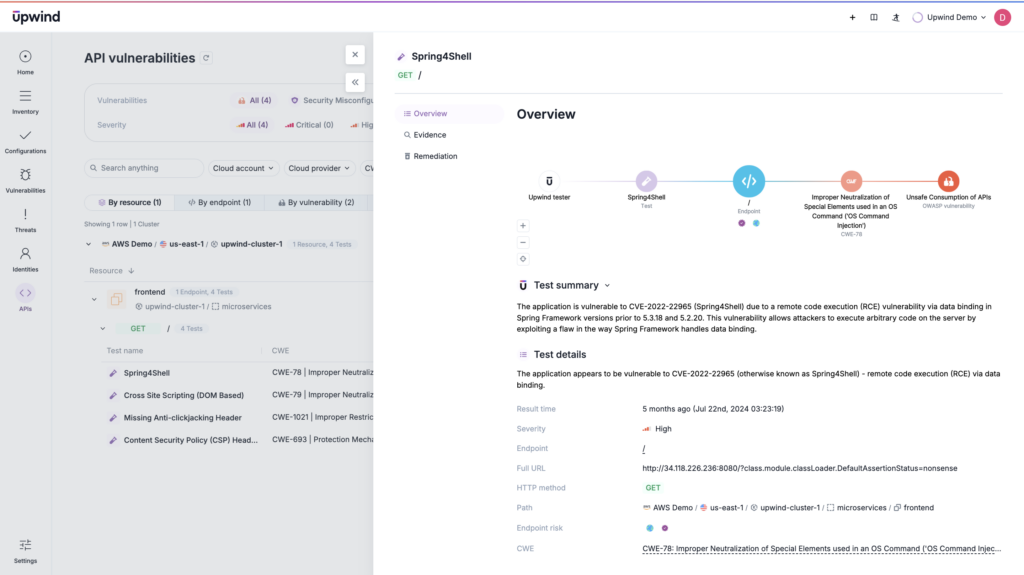
Kubernetes is a powerful solution. One appeal is that it can be customized in multiple ways. This customization makes it very easy to misconfigure the environment, whether through improper access settings or open API endpoints. Any issues in configuration means that the environment is at risk. Closing exposed endpoints isn’t enough on its own, either. Being reachable on the internal network shouldn’t count as permission. Access controls should verify identity and authorization on every request and keep an audit trail.
Runtime Threats
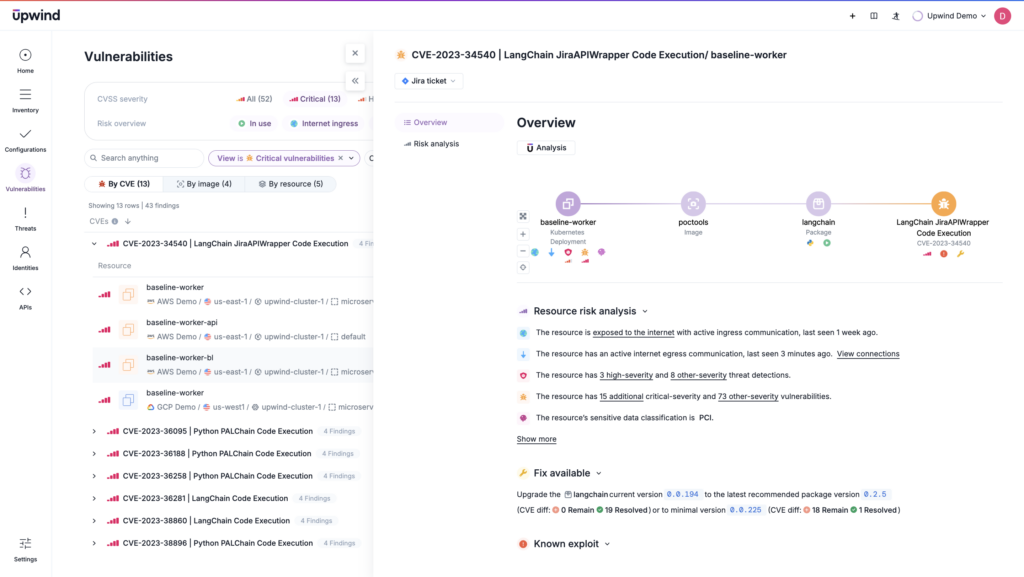
Security vulnerabilities at runtime are some of the most difficult to uncover with scanning solutions. Traditionally, container images are scanned for vulnerabilities prior to deployment. This means issues that don’t emerge until the execution phase – like container escapes or lateral movements – are often left undetected.
Being able to detect and resolve these issues quickly can improve the security of the entire environment.
Infrastructure Vulnerabilities
The underlying infrastructure that supports Kubernetes can be a point of weakness in the system. This could be the cloud platform on which Kubernetes is deployed or the bare-metal server used for a self-hosted environment. For example, if Kubernetes worker nodes are configured with default credentials and exposed to the public internet, attackers can gain access to the underlying servers.
Organizations must ensure that the infrastructure layer is properly secured by restricting access, applying patches, and monitoring cloud provider configurations for any drift or vulnerabilities.
Supply Chain Concerns
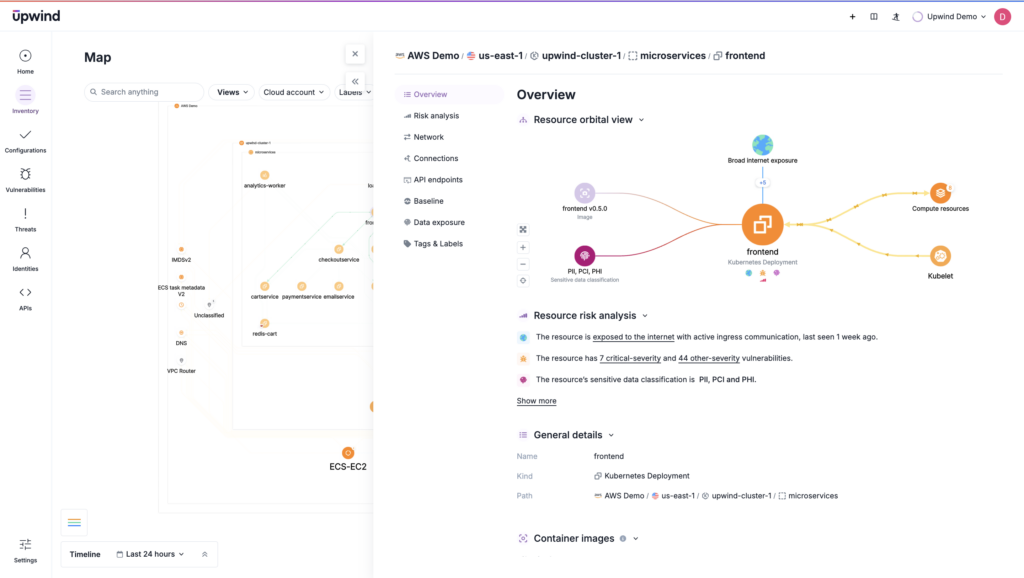
Open-source applications tied into Kubernetes to extend the capabilities of the platform can create new risks. Organizations can use open-source vulnerability management solutions to track any possible software supply chain issues within their Kubernetes environments. They can also employ more comprehensive platforms like cloud-native application protection platforms (CNAPPs) to identify supply chain issues across clouds, explore their unique contingencies and versions, and build remediation into their CI/CD lifecycles. But application dependencies are only part of the picture. In March 2026, attackers compromised Trivy, an open-source security scanner that LiteLLM’s CI/CD pipeline pulled without a pinned version. They used it to steal the project’s PyPI publishing token and published backdoored versions 1.82.7 and 1.82.8 of the litellm package. Supply chain coverage now has to include the security tools, scanners, and package sources running in CI/CD pipelines themselves.
Visibility into the supply chain is a core concern in a Kubernetes environment.
Credential Theft Through Exposed Services
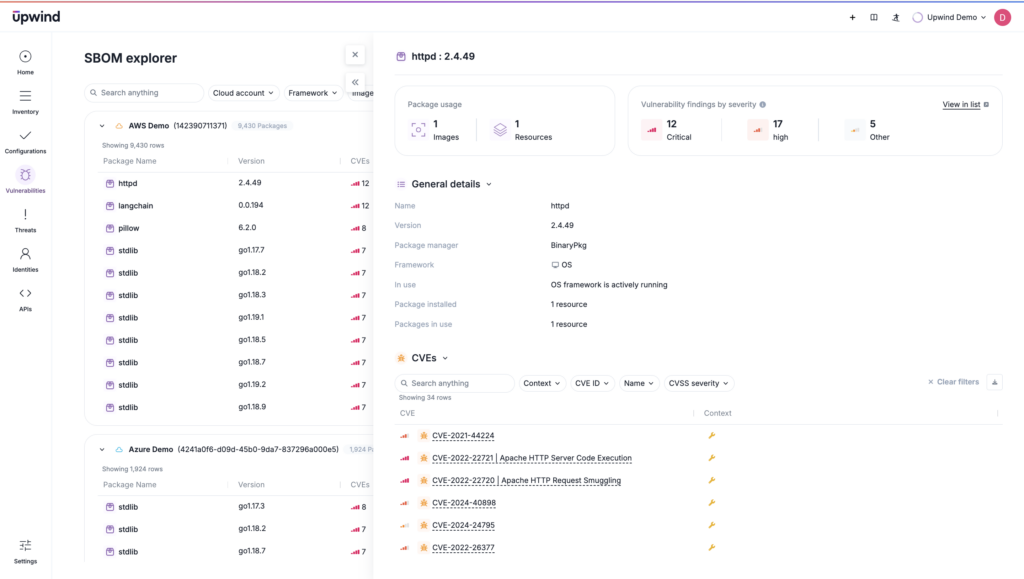
Not every route into a cluster runs through a vulnerable image or a misconfigured API server. In July 2026, QiAnXin’s XLab reported a botnet called NadMesh that hunts exposed AI services such as ComfyUI, Ollama, n8n, Open WebUI, Langflow, and Gradio. What the bots send home includes cloud keys pulled from environment variables, Kubernetes service account tokens, model access, and callable MCP tools. At the time of XLab’s report, most of its observed exploit traffic still went to exposed Docker APIs and Jenkins script consoles, gaps that no patch closes.
That means Kubernetes vulnerability scanning should include discovery of externally exposed services that can reach cluster credentials, not just the cluster and its workloads.
Overcoming Common Scanning Challenges
Kubernetes vulnerability scanning, while key to maintaining a secure environment across all categories of vulnerabilities, comes with its own set of challenges. Those difficulties ultimately complicate team efforts to scan all the categories and lifecycle stages that secure Kubernetes.
What do those look like? Here’s a primer:
| Challenge | What it Means | How to Solve It |
| Performance issues | Kubernetes scanning may slow down deployments if scans are resource-intensive. | Use pipeline-integrated scanning to minimize delays and scan critical workloads first. |
| False positives | Inaccurately tuned scans can generate false positives, overwhelming teams. | Use context-aware tools that consider Kubernetes-specific configurations. |
| Scale management | Scanning large environments with thousands of containers can take too long. | Automate CI/CD-integrated scanning to check containers before deployment. |
| Gaps in coverage | Vulnerability scanners may miss environments if clusters or namespaces are unknown. | Gain multi-cluster and multi-cloud visibility and automatic environment discovery. |
| Resource constraints | Scanners may be allocated too few resources, reducing scan depth or causing failures. | Use autoscaling scanners that dynamically adjust based on load. |
| Dynamic workloads | Containers are constantly created, updated, and deleted, creating blind spots. | Use real-time runtime monitoring to scan containers during operation. |
| Configuration complexity | Misconfigurations can result in security gaps, even with scanned containers. | Use security-as-code practices like policy-based scanning. |
Runtime-powered CNAPPs with shift-left capabilities address many of the hurdles in Kubernetes scanning by automating vulnerability detection, improving scalability, and reducing false positives through context-aware scanning. By integrating directly into CI/CD pipelines, they can also automate scans before deployment, minimizing performance slowdowns while ensuring vulnerabilities are detected early.
This kind of coverage goes beyond traditional IaC scanning, which works statically to scan files for misconfigurations without runtime context. Instead, look for solutions that combine runtime context (like open ports, active workloads, and API endpoints) with pre-deployment scanning.
How to Run a Kubernetes Cluster Scan
A cluster scan works best as a simple, repeatable flow:
- Inventory clusters and namespaces: Identify every cluster you operate and the namespaces inside each one. This sets the scope of the scan and gives you cluster context.
- Scan manifests and admission policies: Review manifests and the rules that govern workload admission for misconfigurations.
- Scan images: Check the layers, dependencies, libraries, and binaries in workload images against known CVEs, using tools like Trivy or Clair.
- Assess nodes: Look for outdated or vulnerable packages on the underlying nodes. Include node findings in the remediation plan, not just container findings.
- Validate runtime exposure: Confirm what is actually exposed in the live cluster, not only what appears in manifests or images. That includes exposed APIs, weak authentication, RBAC issues, and network connectivity.
On managed clusters such as EKS, AKS, or GKE, segment results by cluster so you can tackle each cluster’s most severe findings first.
When results come in, review these first:
- Internet-exposed services
- Privileged pods
- Critical CVEs
- Weak RBAC
- Outdated node packages
Rerun scans whenever clusters, namespaces, images, or policies change, as well as on a schedule, so drift and newly introduced vulnerabilities don’t go unnoticed.
Scanning Across the Application Lifecycle
Remember, truly effective Kubernetes vulnerability scanning doesn’t need to cover just the challenges of workload complexity or bottlenecks; it needs to address these challenges at every stage of the lifecycle.
After all, each stage of the lifestyle, along with each type of vulnerability, introduces its own risks and requires its own scanning capabilities to mitigate issues. Let’s recap what that looks like:
1. Build-Time Security Checks
The foundation of Kubernetes security starts with build-time checks on container images. Scanning container images during development helps teams catch issues like outdated dependencies, critical vulnerabilities, and misconfigurations early.
For instance, a container image with a known CVE in its operating system base layer should trigger an alert and block deployment until patched. Tools like a CNAPP’s CI/CD integration can automate this process.
Paying attention to build-time scanning solves correlated scanning challenges, too:
- Performance issues: Scanning within the CI/CD pipeline prevents bottlenecks by scanning before deployment
- False positives: Even without advanced behavioral analysis, accurate tuning can help avoid excessive alerts during builds
- Scale management: Scanning images one by one during the build process minimizes overwhelming scans at later stages
2. Deployment Validation
Validation during deployment means that containers entering production meet strict security standards. That includes enforcing registry protection policies, verifying that containers are sourced from trusted repositories, and resolving critical vulnerabilities before deployment.
Here’s an example: Kubernetes admission controllers may block pods with unscanned or vulnerable container images. Policy enforcement tools make sure unauthorized workloads aren’t deployed.
Attention at this phase solves for the following scanning challenges:
- Gaps in coverage: Deployment validation means unknown workloads don’t slip through
- Resource constraints: Proper policy enforcement prevents wasting compute resources on unapproved workloads
- Configuration complexity: Automated policy enforcement streamlines complex deployments with interacting services
3. Runtime Monitoring
Some vulnerabilities only emerge at runtime, making real-time monitoring after deployment a must. That’s where runtime monitoring comes in, detecting issues like unexpected process executions, network anomalies, and privilege escalations that static scans miss.
For instance, if a compromised container tries to access restricted Kubernetes services through an unauthorized API call, runtime threat detection tools can block or quarantine the affected pod automatically.
Focusing on runtime helps teams solve scanning challenges like:
- Dynamic Workloads: New or updated containers deployed automatically can be tracked at runtime.
- False Positives: Context-aware monitoring reduces alert fatigue by focusing on real threats, not hypothetical risks.
- Scale Management: Automated scaling includes continuous runtime monitoring, even across thousands of workloads.
4. Continuous Assessment and Remediation
Security isn’t a one-time task — code updates, configuration changes, and zero-day threats emerge all the time. Continuous vulnerability scanning helps detect new vulnerabilities early so clusters stay secure even as workloads evolve.
Ongoing visibility into the cluster’s security posture reduces the risk of undetected breaches.
The scanning challenges solved at this stage are:
- Gaps in Coverage: Automated discovery tools continuously assess new clusters, nodes, and deployments so they’re always on the radar.
- Resource Constraints: Autoscaling scanners make sure that as workloads grow, scanning resources grow, too.
- Configuration Complexity: Regular policy reassessments catch evolving misconfigurations that might not exist at deployment.
Skipping any stage in the application lifecycle increases the attack surface and leaves Kubernetes environments exposed, so Kubernetes vulnerability scanning must handle not just all the categories of vulnerabilities, but the stages of the development lifecycle, too.
How to Compare Kubernetes Vulnerability Scanners
Start by comparing scanners on coverage. Check whether a tool handles images, manifests and Helm charts, cluster configuration, nodes, registries, SBOMs, and runtime context. Then weigh how well it fits your team’s operations:
- False-positive reduction: Prefer context-aware prioritization, exploitability signals, or risk scoring. Some runtime tools, like Falco, may need tuning to cut noise.
- Multi-cluster support: Confirm the tool can monitor multiple clusters and environments.
- Cloud and distro support: Verify support for the platforms you run, such as EKS, AKS, GKE, OpenShift, and VKS. Check operating systems too, such as Amazon Linux, RHEL/UBI, Alpine, Debian, Ubuntu, CentOS, and Oracle Linux.
- CI/CD integrations: Look for scanners that run in pull requests, builds, and test pipelines.
- Policy enforcement: Check whether the tool can validate, mutate, generate, or enforce policy.
- Reporting: Prioritize auditable inventories, posture views, and clear reports.
Here’s a vendor-neutral look at common tool categories:
| Category | Examples |
| Manifest and Helm chart scanners | KubeLinter |
| IaC and Kubernetes policy/compliance scanners | Checkov |
| Multi-purpose vulnerability and misconfiguration scanners | Trivy |
| End-to-end posture platforms | Kubescape |
| Image signing and verification tools | Cosign/Sigstore |
| Policy enforcement engines | Kyverno, OPA Gatekeeper |
| Runtime detection tools | Falco |
| Networking and network-policy tools | Cilium, Calico |
A single-purpose scanner makes sense when the job is narrow, such as manifest linting with KubeLinter or runtime detection with Falco. Focused tools like these are quick to drop into CI/CD.
A broader platform makes sense when you need coverage across lifecycle stages and combined visibility into manifests, live clusters, and runtime. It also fits teams that want centralized reporting and risk scoring. No single tool covers everything, though. Most teams end up layering shift-left scanning, policy enforcement, runtime protection, registry checks, and compliance auditing.
Upwind Solves for Kubernetes Vulnerability Scanning
Upwind’s real-time vulnerability detection across multi-cloud and multi-architecture environments helps security teams automatically detect and prioritize the vulnerabilities that pose the biggest risks. With runtime intelligence, Upwind precisely identifies critical risks and enables focused, efficient, and intelligent security. And with integration into the CI/CD lifecycle, Upwind shifts left to cover built-time vulnerability remediation as well.
To learn more about Upwind’s vulnerability management solution, request a demo today.
Frequently Asked Questions
How often should Kubernetes environments be scanned?
According to security best practices, Kubernetes environments should be scanned for vulnerabilities at least daily, ideally as part of your continuous integration and continuous deployment (CI/CD) pipeline, to catch potential security issues early in the development cycle and ensure timely remediation. Scanning should include container images, configurations, and cluster components.
What’s the difference between image and runtime scanning?
Not all Kubernetes scanning includes containers. Image scanning involves inspecting the container image itself during build-time for any potential vulnerabilities. But that won’t help teams identify problems in the Kubernetes environment.
Runtime scanning involves identifying vulnerabilities in containers and processes in the live environment. Scanning focuses on real-time attacks, anomalies, and system behavior rather than for known vulnerabilities.
How do you handle scanning in multi-cluster environments?
Kubernetes clusters include the control plane, nodes, pods, networking, and storage: in other words, they encompass workloads, machines that run containers, and the systems managing that workload.
Adopting an event-driven approach to multi-cluster environments means adopting centralized management to apply consistent security policies, automate scanning across clusters, and aggregate findings in a single dashboard. Runtime monitoring tools and runtime-powered CNAPPs are key, since teams who manage multi-cluster environments will need to automatically discover new workloads, enforce policies, and continuously monitor those clusters for vulnerabilities and threats.
What role do vulnerability scanners play in compliance?
Vulnerability scanners play a critical role in compliance. Here are the core ways they help:
- Risk Identification: They detect security vulnerabilities, misconfigurations, and policy violations across containers, infrastructure, and applications.
- Compliance Checks: Vulnerability scanning is a required part of meeting compliance requirements in regulatory frameworks like PCI-DSS, GDPR, HIPAA, SOC 2, ISO 27001, and CIS Benchmarks.
- Audit Readiness: They generate detailed compliance reports for audits, showing scan results, remediation actions, and policy enforcement.
- Continuous Monitoring: They provide real-time scanning to maintain compliance even as new vulnerabilities emerge.
- Policy Enforcement: Scanners can apply security policies automatically to ensure that workloads meet compliance standards before deployment.
- Remediation Tracking: Scanners track vulnerability fixes and patch updates so violations get fixed quickly.
How do you prioritize vulnerability remediation in Kubernetes?
There are multiple ways to tackle vulnerability prioritization. Organizations can use:
- Common Vulnerability Scoring System (CVSS) scores
- Insight into exploitability
- Business impact
- Exposure in the Kubernetes context
- Criticality given runtime context
- Compliance requirements
Ultimately, filtering the criticality of vulnerabilities is a multifaceted job. Combining known vulnerability risks with the runtime environment is key to taming the alert overload and addressing truly critical vulnerabilities first.
How do you secure Kubernetes cluster nodes by scanning them for vulnerabilities?
Scan nodes broadly, beyond default ports, and probe service responses to confirm what’s actually running. Look for vulnerable services, exposed control panels, misconfigurations, and Kubernetes-specific components like cAdvisor. Prioritize findings by CVSS v3 severity, and run scheduled scans with diff comparisons to catch regressions. Pair node scanning with pre-deployment image scans and node hardening, such as minimizing the OS, removing unused accounts and software, and using AppArmor or SELinux.