A red flag with a circular arrow design featuring the letters DNS waves against a blue cloudy sky. The word Upwind is displayed in the top left corner.

Detect Suspicious Communication with a Public DNS Resolver 

Denise Ashur May 08, 2024

Detect Suspicious Communication with a Public DNS Resolver 

We are excited to announce a new capability to detect unusual DNS resolver activity.

This detection notifies you of unusual behavior by a virtual machine or container in your cloud environment, which is communicating with a public DNS resolver that it hasn’t communicated with recently.

DNS Resolvers

Trusting your DNS resolvers is a critical part of your overall security hygine, since this is the component that maps out IP addresses for hosts connected to the Internet.

Indicators of Compromise

Due to its important nature, DNS resolution issues are often the cause of network outages. Errors such as misconfigurations in a single DNS server can cause widespread communication failures for all services that communicate with it, and they are typically very difficult to identify since teams often need to investigate each server individually in order to find issues.

DNS is also the focal point or frequent target for many attacks, due to its important role in internet communication. Attackers can hijack resources and cause them to communicate with a public DNS resolver in attempts to gain access to an environment or steal data.
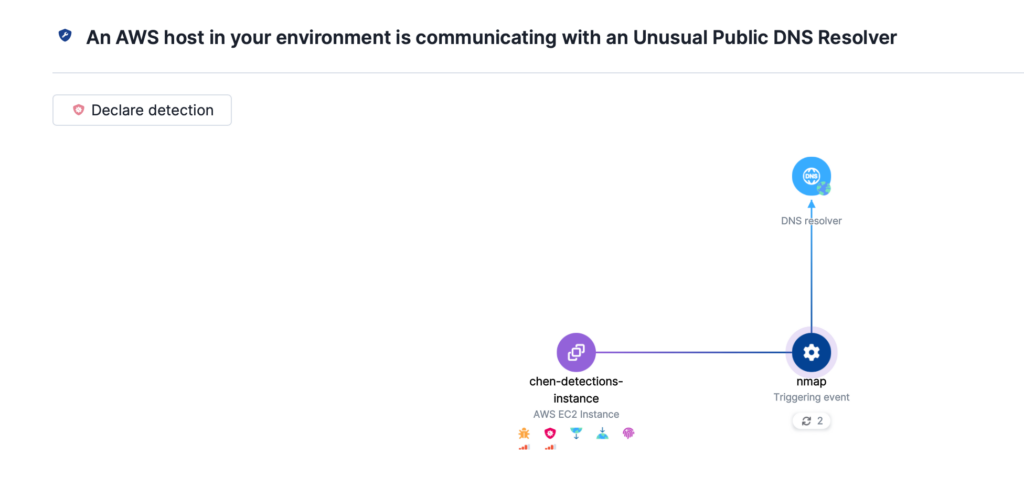
Screenshot-2024-05-03-at-6.37.27%E2%80%AFAM-1024x477

This detection notifies you of unusual behavior by a virtual machine or container in your cloud environment, which is communicating with a public DNS resolver that it hasn’t communicated with recently. This is suspicious because it deviates from the established baseline behavior of the resource within the environment and may indicate an attempt to use alternative DNS resolvers for bypassing network monitoring, exfiltrating data, or other malicious activities aimed at evading detection.

Upwind leverages runtime data to rapidly identify unusual DNS resolver communication and immediately alert you to suspicious activity. Read more about DNS resolver detections in the Upwind Documentation Center (login required).
Contents

Further Reading

Let Me Speak to Your Manager (Account)

Let Me Speak to Your Manager (Account)

The management account is the most privileged account in any AWS Organization. It controls SCPs, creates and deletes member accounts, manages IAM Identity Center, and is itself exempt from SCPs. Getting its 12-digit account ID is the first step in targeting it. The documented way to get it is organizations:DescribeOrganization - but security-conscious environments restrict…
Configuration-Focus

Introducing the new Configurations experience in Upwind

Compliance should not be a fire drill! Ask a security team how audit season goes and you will often hear a version of the same story. Someone pulls a list of cloud accounts. Someone else exports findings into a spreadsheet that is already outdated by the time it is shared. Screenshots get pasted into a…
What You Could Build If IAM Let You

What You Could Build If IAM Let You: New Policies From Undocumented Condition Keys

In the previous post, we mapped 36 condition keys that the IAM engine evaluates but has never documented. The decomposition model, the service-specific resource identifiers, the organizational metadata - all of it sitting in the request context, invisible unless you probe for it. That post was about discovery. This one is about what you can…
Add the Upwind RSS Feed to Slack
Connect the Upwind RSS Feed to your Slack.
Follow the how-to here.
Threat RSS
Add the Upwind RSS Feed to Slack
Connect the Upwind RSS Feed to your Slack.
Follow the how-to here.
Main RSS