
A critical Remote Code Execution (RCE) vulnerability identified as CVE-2024-21534 has been discovered in versions of the jsonpath-plus package before 10.0.0. This vulnerability allows attackers to execute arbitrary code on affected systems by exploiting improper input sanitization and the unsafe default usage of the vm module in Node.js. jsonpath-plus is a JavaScript implementation of JSONPath with additional operators, widely used for querying and manipulating JSON data in Node.js applications. Unfortunately, versions prior to 10.0.0 are vulnerable due to improper input handling, which can be exploited to execute malicious code.
Vulnerability Details
The vulnerability arises from the unsafe default usage of the Node.js vm module within jsonpath-plus. Specifically, the package fails to properly sanitize user inputs, allowing attackers to inject and execute arbitrary code on the server.
Even after the release of version 10.0.0, which mitigated the vulnerability by changing the default behavior, the unsafe functionality remains available but is no longer enabled by default. This means systems that have not updated or have re-enabled the unsafe behavior are still at risk.
Proof of Concept (PoC)
An attacker can craft a malicious JSONPath expression that includes arbitrary JavaScript code. When this expression is evaluated by jsonpath-plus, the injected code executes on the server. Here’s how the exploitation process works:
- Malicious Input Crafting: The attacker creates a
JSONPathexpression that embeds JavaScript code intended to perform unauthorized actions, such as reading sensitive files or executing system commands. - Injection Point: The malicious
JSONPathis supplied to an application endpoint that utilizesjsonpath-plusto process user-provided queries on JSON data. - Code Execution: The application evaluates the expression using the vm module without proper sanitization. This leads to the execution of the attacker’s code on the server.
When this code is run (node index.js), it executes the cat /etc/passwd command, displaying the contents of the /etc/passwd file. This demonstrates how an attacker could execute arbitrary system commands.
// index.js
const { JSONPath } = require("jsonpath-plus");
const data = {};
const maliciousCode = 'require("child_process").exec("cat /etc/passwd")';
const maliciousPath = `$[(this.constructor.constructor("${maliciousCode}")())]`;

const result = JSONPath({
    json: data,
    path: maliciousPath
});
Impact
- Unauthorized Access: Attackers can gain unauthorized access to your system.
- Data Breach: Sensitive information could be exposed or stolen.
- System Compromise: Full system compromise leading to service disruptions or further attacks.
Recommended Actions
To protect your system from this critical vulnerability, it is essential to:
- Update the
jsonpath-plusPackage: Upgrade to version10.0.0or later where the default behavior has been changed to be safer. - Audit Your Codebase: Check for any custom configurations that might re-enable the unsafe functionality and adjust them accordingly.
- Sanitize Inputs: Always ensure that user inputs are properly sanitized to prevent injection attacks.
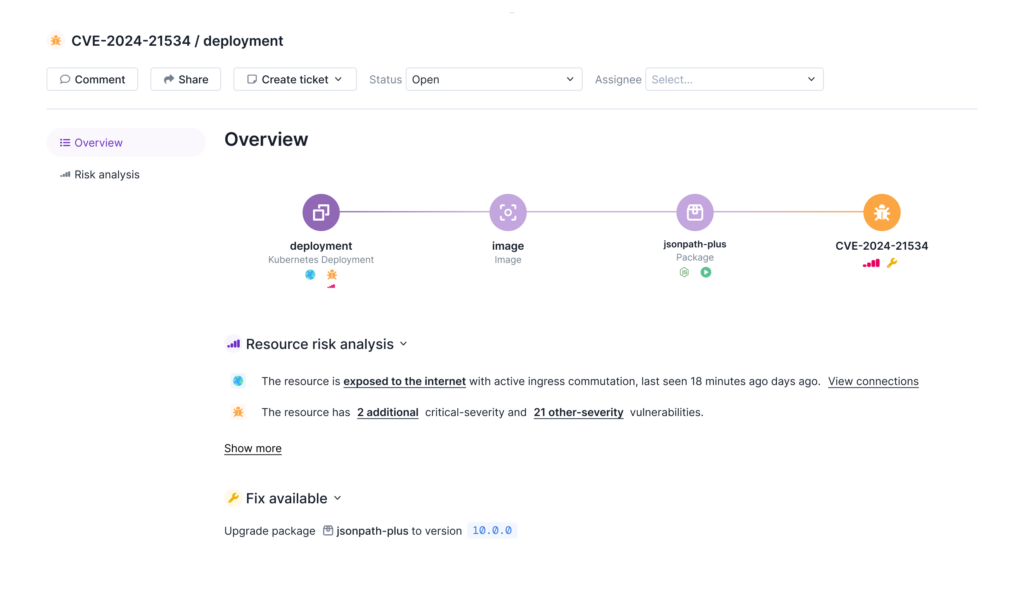
How Upwind Helps Protect You From the jsonpath-plus Vulnerability
Upwind Cloud Security Platform provides comprehensive protection and vulnerability management, offering tools to identify and mitigate risks from this vulnerability:
- SBOM Explorer: Use Upwind’s SBOM Explorer to locate all instances of
jsonpath-plusin your environment and check which versions are affected by this vulnerability. - Vulnerable Resource Detection: Identify all resources in your environment running vulnerable versions of
jsonpath-plus, and assess which clusters, VMs, and resources are exposed to this vulnerability. - Risk Context: Understand the potential impact of this vulnerability on your system, particularly in environments with sensitive data, internet exposure, or communication with critical services.
- Prioritize Fixes: Upwind helps you prioritize patching or updating vulnerable resources, streamlining the process to secure your environment against this RCE vulnerability.
Get Further Help from Upwind
Upwind’s expert security team also provides 24/7 managed detection and response services, giving you real-time support for CVE-2024-21534 and all critical vulnerability findings. For additional help finding vulnerable packages, identifying the scope of resource usage with the CVE, understanding their risk context and prioritizing package upgrades contact the Upwind MDR team at [email protected] or schedule a demo.